
GENERAL MEETINGS
MN ISSA holds its meetings on a quarterly basis and they generally have 2 speakers and networking opportunities. Typically chapter meetings are held the 3rd or 4th Tuesday of March, June, and September. Doors open 30 minutes prior to the start time (except virtual meetings) The 4th meeting of the year is the 'End of Year Cheer' multi-association, held in November, in partnership with other affiliates, such as the Minnesota Chapters of WiCyS, InfraGard, and the MCPA.
You are welcome to join us as a guest if you’re not currently an MN ISSA member! If you find value in attending our meetings and want to continue to participate, then we do ask that you become an ISSA member. Your membership provides great benefits to you and helps provide the funding needed to keep our chapter going. We appreciate it!
These meetings will rotate locations throughout the metro to align to our goal of reaching as many people as possible.
AFTER HOURS
Our After Hours format is more casual and interactive than our regular chapter meetings and is designed for those not always able to make regular meetings, for individuals from our larger local security community, as well as those who simply enjoy discussion with their peers and industry leading thinkers. Our After Hours events are typically Members Only, and are held on the last Tuesday of a month. The months will fluctuate based on Chapter Meetings, Holidays, etc., so check the website or watch social media for After Hours event updates.
Come out and join us – you’ll get informative presentations in intimate settings at great local venues, good food and refreshments, plus plenty of opportunity to refresh and build your network with valuable connections.
WEBINARS
Virtual seminars and webinars are offered to MN ISSA members and feature industry and subject matter experts from Minnesota and throughout the United States. The webinars allow us to expand on topics and discussions from chapter meetings, or explore new and emerging trends, impactful events, or requested content from our members and community. The format and structure change with the subject and webinar speakers, so be sure to check the event details for webinar details, links, and virtual session information.
Meeting/Event Information
September 23rd Chapter Meeting
September 23, 2025
2:30 PM - 5:00 PM
Add to Calendar
Wooden Hill Brewing Company
7421 Bush Lake Rd, Edina, MN 55439
Edina, MN 55439
Venue website
Directions
Managed Service Providers - Maximizing Trust Without Introducing Risk
Identity, Resiliency, Automation. While all are critical to an organization’s Security Operations, these risk priorities are not necessarily harmonious. Many organizations are increasingly turning externally to Managed Service Providers, for value-based access to their critical corporate and industry experience and expertise, and opportunities to drive process efficiency.
However, as MSP partnerships increasingly become more holistic and proactive, this dependency also leads to a new frontier of challenges, for both parties. For instance:
- In many cases, a trusted MSP is as highly aware as their customer when it comes to the organization’s Identity Security, the potential for compromise and 3rd party risk.
- Expectations between organizations and their MSP partners to automate processes while maintaining security posture can gradually or suddenly drift into misalignment.
- MSP partners assume significant responsibility and risk when it comes to shared compliance with their customers - mistakes are not an option!
Please join us as we ‘round third base’ for our Q3 Chapter Meeting on Tuesday, September 23rd, when we will pan out our focus slightly to the highly valuable partners who extend our ability to fortify our IT environments through growth and change, and the immensity of the accompanying shared responsibility. Our subject-matter experts from ‘both sides of the table’ will share and debate the challenges associated with partnering to move at the speed of business while at the same time adopting, enforcing - and sharing - a security-first mindset.
We cannot seem to break our fixation on Wooden Hill Brewing in Edina, which to-date offers unmatched comfort, premium audio quality and delicious cuisine for our outstanding TC’s security community.
Our Panelists:
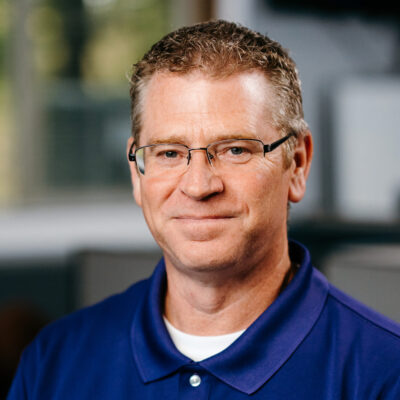
Jeff Saucier, Chief Information Security Officer, Point North Networks
Jeff’s rich experiences, spanning over 30 years, remarkably touch upon all aspects of the IT lifecycle - datacenter, network, server, desktop, security, compliance, and technical support. In his current role as CISO, Jeff supports the mission of Point North Networks to provide high-quality Managed IT, Cyber Security, and Private Cloud Hosting Services to clients throughout the Twin Cities and across the country.
Jeff’s vast background features the design and operations of highly complex systems, as well as the leadership and coordination across key stakeholders and teams. Prior to Point North, Jeff worked for over 11 years as Vice President of IT for Westwood Professional Services, a national engineering services provider for private development, public infrastructure, wind energy, solar energy, and power delivery projects, established in 1972 in Minneapolis. Prior to Westwood, Jeff held extensive roles with Dolan Media Company and 3M.
His education includes an Associates Degree in Computer Operations at Century College - where Kristy Livingston currently teaches!
Kristy Livingston, MS EnCE, Adjunct Professor - Digital Forensics, Century College
Kristy is a collaborative and innovative information security leader with broad expertise around security engineering and operations. As Adjunct Professor at Century College, Kristy empowers and inspires her students to work towards their career goals and prepare them to take the first steps into the field of Digital Forensics.
Kristy has 15 years of information security experience and has held leadership roles with oversight for data governance, vulnerability management, e-discovery and incident response teams. Kristy holds a Master of Science in Secure Technologies (MSST) from the University of Minnesota Technological Leadership Institute and maintains industry certifications including CISSP and EnCE.
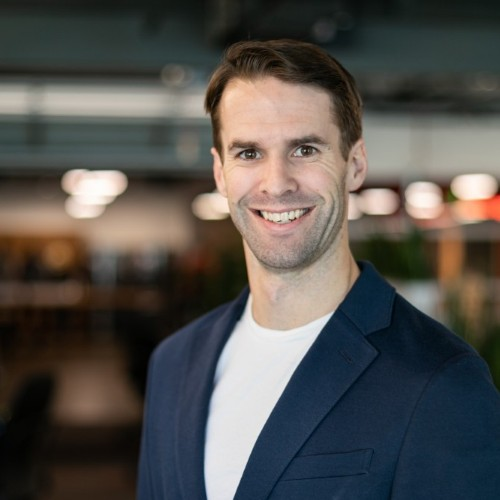
Chris Brown, Vice President, Point Solutions Security
In his role at PSS, Chris supports client projects on cyber service operations, pen testing, red teaming, compliance, systems integration and security assessment. Chris also works as a Strategic Advisor to Sittadel, a cybersecurity platform specializing in Microsoft Security. Chris’ expertise includes Zero Trust, Device Security and Risk Assessment. Prior to Point Solutions Security, Chris held consulting roles with Expel MDR and Red Canary.
Hailing to us from Denver, Colorado, Chris demonstrates a distinctive ability to communicate complex concepts clearly, create excitement and unite teams around common business objectives.

Daniel Cunningham, Manager, IT Security, Prime Therapeutics
Dan is an experienced Information Technology and Security Supervisor with a demonstrated history of working in the mechanical and industrial engineering industries. Prior to his current role, Dan led cyber incident management at 3M, and cyber engagement planning for the Minnesota National Guard. Commissioned a Second Lieutenant in 2002, Lieutenant Colonel Cunningham was the first commander of the Minnesota Cyber Protection Team. He has completed deployments to Bosnia in 2003-2004 and Iraq in 2006-2007 and 2009-2010, earning a Bronze Star Medal with a bronze oak leaf cluster.
Dan is an active leader in the TC’s Information Security community, former Co-Chair of the Cyber Security Summit, and volunteer with the local chapter of Military Cyber Professionals Association.
Our Moderator:
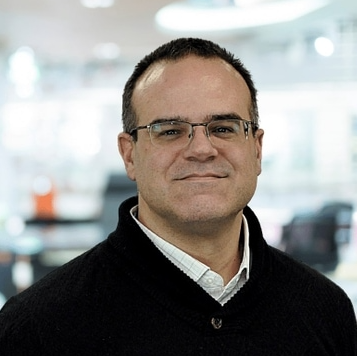
Paul Veeneman, President, MN ISSA
With nearly 30 years of experience across various industries including Oil and Gas, Healthcare, Energy, Renewables, and Manufacturing, Paul works within United States critical infrastructure, addressing challenges and providing guidance in OT, ICS, IoT, IIoT, and SCADA cyber security knowledge, expertise, and education.
Paul currently holds the CISSP, CISM, and CRISC certifications, and serves on several boards in addition to MN ISSA, including Minnesota chapters of International Society of Automation (ISA), and the InfraGard Member Alliance.
Meeting Agenda:
2:30pm: Arrival
2:45pm: Greetings & Announcements
3pm: Panel Discussion: Managed Service Providers - Maximizing Trust Without Introducing Risk
3:40: Sponsor Spotlight: Abnormal AI
3:50: Break
4pm: Panel Discussion Real-World Scenario - O365 Email Attacks
4:45: Wrap Up
5pm: Hosted Happy Hour!
This Meeting and Happy Hour is brought to you by our valued Sponsor, Abnormal AI.

Please register and mark your calendar now, and as usual, look for updates via email and this web page. See you then!
Tickets
$0.00 Board Member Registration
$0.00 Chapter Sponsor Registration
$0.00 MN ISSA Member Registration
$0.00 Non-Member Registration
FAQs
Are non-members and guests welcome at meetings and events?
Yes, we welcome individuals at large from the security community to join us for any of our events. We simply ask that, after experiencing the value of our community at two events, individuals consider joining ISSA for the additional benefits that membership provides.
Why do we have to register to attend meetings and events?
Besides assisting the board with planning logistics for our events, registering for meetings and events, provides you with self-service documentation you can print out to support your CPE credits if you are audited.
Disclaimer
By registering for this event, I agree that:
- I am allowing my contact information included in the registration to be shared with MN ISSA and I may be contacted by MN ISSA
- I grant MN ISSA and/or ISSA International the right to use any candid photos or videos taken during the event in future marketing and communication efforts, to include, but not limited to, websites, brochures, advertisements, magazines, newspapers, newsletters, emails, videos and web conferences.
- If this is a joint chapter meeting with another local security organization, my basic information (name, email) will be shared with the other organization.
