
GENERAL MEETINGS
MN ISSA holds its meetings on a quarterly basis and they generally have 2 speakers and networking opportunities. Typically chapter meetings are held the 3rd or 4th Tuesday of March, June, and September. Doors open 30 minutes prior to the start time (except virtual meetings) The 4th meeting of the year is the 'End of Year Cheer' multi-association, held in November, in partnership with other affiliates, such as the Minnesota Chapters of WiCyS, InfraGard, and the MCPA.
You are welcome to join us as a guest if you’re not currently an MN ISSA member! If you find value in attending our meetings and want to continue to participate, then we do ask that you become an ISSA member. Your membership provides great benefits to you and helps provide the funding needed to keep our chapter going. We appreciate it!
These meetings will rotate locations throughout the metro to align to our goal of reaching as many people as possible.
AFTER HOURS
Our After Hours format is more casual and interactive than our regular chapter meetings and is designed for those not always able to make regular meetings, for individuals from our larger local security community, as well as those who simply enjoy discussion with their peers and industry leading thinkers. Our After Hours events are typically Members Only, and are held on the last Tuesday of a month. The months will fluctuate based on Chapter Meetings, Holidays, etc., so check the website or watch social media for After Hours event updates.
Come out and join us – you’ll get informative presentations in intimate settings at great local venues, good food and refreshments, plus plenty of opportunity to refresh and build your network with valuable connections.
WEBINARS
Virtual seminars and webinars are offered to MN ISSA members and feature industry and subject matter experts from Minnesota and throughout the United States. The webinars allow us to expand on topics and discussions from chapter meetings, or explore new and emerging trends, impactful events, or requested content from our members and community. The format and structure change with the subject and webinar speakers, so be sure to check the event details for webinar details, links, and virtual session information.
Meeting/Event Information
June 23rd Chapter Meeting
June 23, 2026
2:30 PM - 5:00 PM
Add to Calendar
Wooden Hill Brewery
7421 Bush Lake Road
Edina, MN 55439
Venue website
Directions
Generative AI adoption is outpacing the governance and security controls most organizations have in place to manage it. Employees are using AI tools to draft documents, analyze data, write code, and automate workflows, often through channels that fall outside traditional IT visibility. Vendors are embedding AI capabilities into existing products, sometimes without clear disclosure. Meanwhile, the threat landscape is evolving in parallel, with adversaries leveraging the same technologies to scale phishing, social engineering, and reconnaissance.
- Discovering Shadow AI in Your Environment — Identifying unsanctioned AI usage across SaaS platforms, browser extensions, and embedded vendor features, and understanding where sensitive data may already be flowing to third-party models.
- Establishing Practical AI Governance — Building acceptable use policies, approved tool inventories, and data classification guidance that integrate with existing security, privacy, and records management programs rather than operating in parallel to them.
- Evaluating Vendor and Third-Party AI Risk — Adapting existing vendor risk processes to account for model provenance, training data handling, output reliability, and contractual protections specific to AI-enabled products and features.
- Protecting Data at the Prompt — Addressing the most immediate and frequently realized risk: sensitive data, intellectual property, and regulated information disclosed through user prompts to public or semi-public models.
- Securing Internal AI Deployments — Considerations for organizations building or integrating AI capabilities directly, including access controls, logging, prompt injection, and the security implications of agentic systems and connected tools.
- Preparing for AI-Enabled Threats — Practical adjustments to detection, awareness training, and incident response in light of deepfake social engineering, AI-assisted phishing at scale, and emerging adversarial techniques.
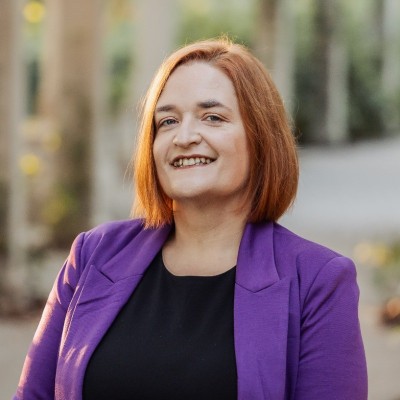
Mea Clift is the Chief Information Security Officer (CISO) at Cengage, a seasoned cybersecurity executive known for aligning security strategy with enterprise risk and resilience. With decades of experience, she specializes in governance, risk, and compliance (GRC), helping organizations navigate complex threats and translate technical risk into clear business value.
A 2025 honoree of the Women in IT Security awards, Mea is widely recognized for her leadership, mentorship, and advocacy for diversity in cybersecurity. Mea is also the creator of the GRC Intensive Program, a 14 week hands-on educational program to teach the how of GRC to cybersecurity practitioners.
She joins Cyber Mettle to help open opportunities for GRC professionals, but also to help advise organizations needing a better understanding of cyber risk that may be at or below the cybersecurity poverty line. With an organization like Cyber Mettle, she hopes that we can help move the needle forward on protecting small, underfunded and underrepresented businesses, municipalities, and more while also creating better pipelines to entry in the cybersecurity field.
Outside of her professional work, she is a passionate quilt historian and educator, and lives in St. Paul, Minnesota, with her dogs (notably her greyhounds), combining her love of textiles with a deep commitment to community and creativity.
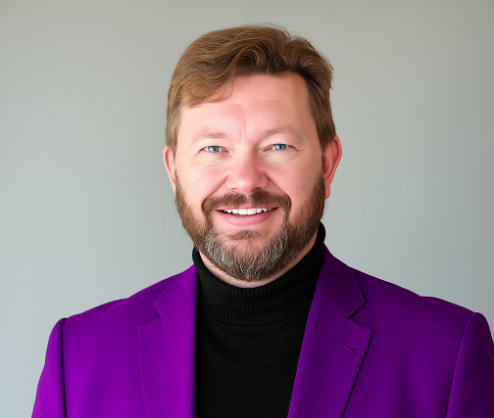
In 2017, he was appointed by Governor Doug Burgum as North Dakota’s Chief Information Officer and Cabinet Member, where he redefined what “government technology” could be and led nationally recognized innovation efforts.
Today, Shawn serves as the CEO of Bisblox, a global Venture Studio building companies designed to be bold, disrupt boring, and strengthen growth. Through Bisblox, he continues to champion a simple guiding question: “How might we help others succeed?”
With over a thousand stages under his belt, Shawn is a widely known keynote speaker and mentor, passionate about helping leaders and founders navigate technology, transformation, and the human side of innovation.
Tickets
$0.00 Board Member Registration
$0.00 Chapter Sponsor Registration
$0.00 MN ISSA Member Registration
$0.00 Non-Member Registration
FAQs
Are non-members and guests welcome at meetings and events?
Yes, we welcome individuals at large from the security community to join us for any of our events. We simply ask that, after experiencing the value of our community at two events, individuals consider joining ISSA for the additional benefits that membership provides.
Why do we have to register to attend meetings and events?
Besides assisting the board with planning logistics for our events, registering for meetings and events, provides you with self-service documentation you can print out to support your CPE credits if you are audited.
Disclaimer
By registering for this event, I agree that:
- I am allowing my contact information included in the registration to be shared with MN ISSA and I may be contacted by MN ISSA
- I grant MN ISSA and/or ISSA International the right to use any candid photos or videos taken during the event in future marketing and communication efforts, to include, but not limited to, websites, brochures, advertisements, magazines, newspapers, newsletters, emails, videos and web conferences.
- If this is a joint chapter meeting with another local security organization, my basic information (name, email) will be shared with the other organization.
